DeepSec Consulting | DPDP Act & GRC Series
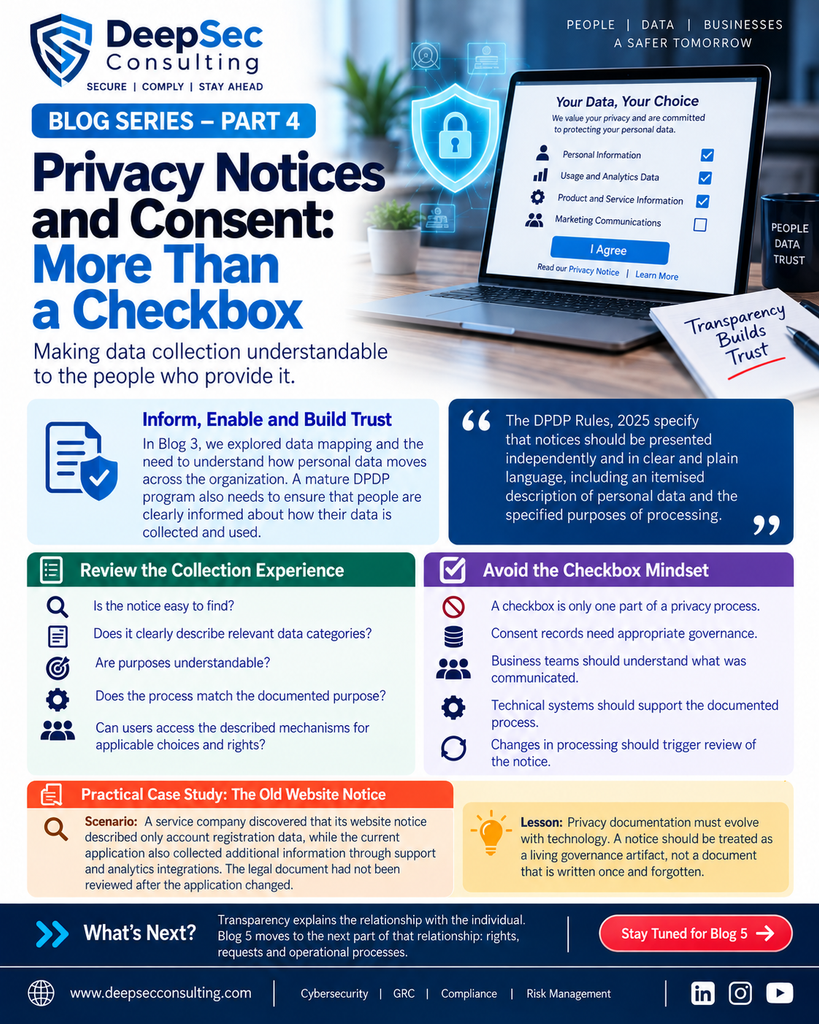
In Blog 3, we explored data mapping and the need to understand how personal data moves across the organization. But knowing where data exists is only part of the picture. A mature DPDP program also needs to ensure that people are clearly informed about how their data is collected and used.
The DPDP Rules, 2025 specify that notices should be presented independently and in clear and plain language, including an itemised description of personal data and the specified purposes of processing. The Rules also address ways for Data Principals to access information and exercise relevant choices.
This means organizations should compare their notices with actual technical and business processes. A privacy notice that says one thing while the application does another creates a governance problem.
Review the Collection Experience
- Is the notice easy to find?
- Does it clearly describe relevant data categories?
- Are purposes understandable?
- Does the process match the documented purpose?
- Can users access the described mechanisms for applicable choices and rights?
Avoid the Checkbox Mindset
- A checkbox is only one part of a privacy process.
- Consent records need appropriate governance.
- Business teams should understand what was communicated.
- Technical systems should support the documented process.
- Changes in processing should trigger review of the notice.
Practical Case Study: The Old Website Notice
Scenario: A service company discovered that its website notice described only account registration data, while the current application also collected additional information through support and analytics integrations. The legal document had not been reviewed after the application changed.
Lesson: Privacy documentation must evolve with technology. A notice should be treated as a living governance artifact, not a document that is written once and forgotten.
Transparency explains the relationship with the individual. Blog 5 moves to the next part of that relationship: rights, requests and operational processes.
DeepSec Consulting can help organizations assess DPDP readiness, identify privacy and security gaps, and build a practical GRC roadmap aligned with their business environment.
No comments